

#dev 2024-11-14
2024-11-14 UTC
AcesAndEights, gRegor, [Askan]1, __DuBPiRaTe__, GuestZero_, [tw2113], [morganm]2, [snarfed]2, jjuran_, Xe, Cadey, GuestZero, jeremych-, Dryusdan, glacier, [juliaro], [manton] and AramZS joined the channel
#  [Murray] I'm not too sure what to think about this. JS-reliant, but interesting. Would love to see some more practical examples: https://www.wearedevelopers.com/magazine/micro-components---an-alternative-to-web-components-and-frameworks#toc-0

[schmarty], barnaby and sebbu joined the channel

[qubyte] joined the channel
#  [qubyte] It’s built for my setup, but in case anyone needs some example code (particularly for the auth flow and the post payload composition), here’s my github action workflow and a script to syndicate notes with images and links/bookmarks in jf2 format to Bluesky. I’m not really happy that Bluesky is grabbing so much mind share, but I don’t mind supporting it for POSSE. https://github.com/qubyte/qubyte-codes/pull/1059
#  capjamesg[d] [qubyte] OpenAI publishes Content Credentials, which you could use to build an extension to filter out images.
# capjamesg[d] But that would only work for DALL-E images.
# capjamesg[d] Or any edited with AI in Photoshop!
gRegor and [Sophia_wood] joined the channel
# capjamesg[d] Content Credentials are metada.
# capjamesg[d] *metadata
# capjamesg[d] Photoshop adds them to images edited with AI, as does OpenAI when you generate one.
kerem joined the channel
barnaby, Julia and [aciccarello] joined the channel
#  [snarfed]2 defaults matter, 99% is still useful, but you're right, content creds/C2PA don't "solve" this for all images
# [snarfed]2 ...but for specific individual images that are important and need verification, if those images use C2PA, it can provide a meaningful guarantee that they either were or weren't AI-generated
# [snarfed]2 the usual example is, if a photo is genuine and people want to use it as evidence for something, C2PA can prove that it's real and not AI-generated or modified
# capjamesg[d] ^^
# [snarfed]2 just fyi [gRegorLove]
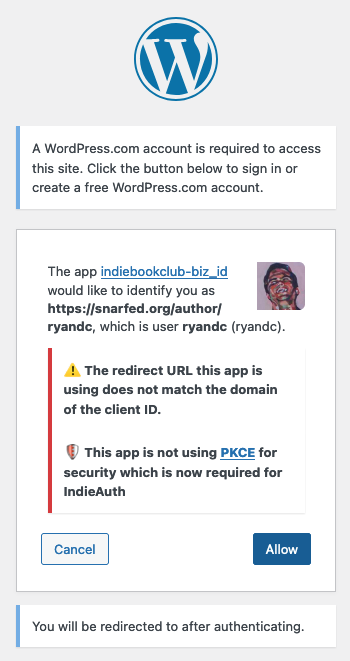
# [snarfed]2 interesting, https://indielogin.com/ has the same problem

#  Loqi aaronpk: gRegor left you a message 23 hours, 10 minutes ago: I get the allowed client_id for IBC updated in indielogin? It's been `https://indiebookclub.biz/id` for a bit now, but just realized today it was preventing some people from signing in since indielogin has it without the "/id"

# [snarfed]2 [gRegorLove] still getting the same error on https://indiebookclub.biz/ . cc GWG, this ^ is with the WP IndieAuth plugin v4.5.2
# [snarfed]2 GWG I'm getting the "The authorization header was not returned on this test, which means that your server may be stripping the Authorization header." warning on my site health, so maybe that's the problem? not sure though
[pfefferle] joined the channel
# [Joe_Crawford] [gRegorLove] That seemed to work!
__DuBPiRaTe__, CRISPR, barnaby and bterry joined the channel